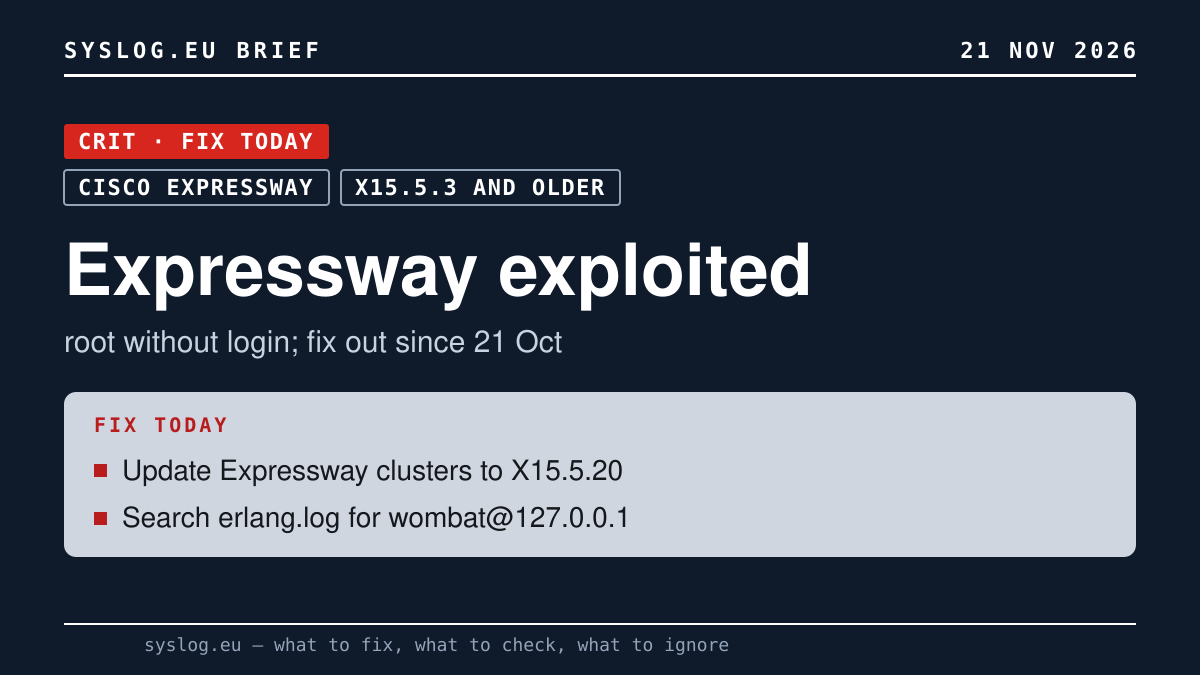
Does this concern you?
- Affected: anyone running Cisco Expressway-C or Expressway-E, virtual or appliance, configured in a cluster and on X15.5.3 or earlier.
- Skip it if: you run no Expressway, or your Expressway devices are not in a cluster; Cisco lists only clustered devices as vulnerable.
What to do
- Check the release of each node and upgrade X15 nodes to X15.5.20 or later. Cisco says nodes on X14 or earlier must migrate to a fixed release. There is no workaround.
- Look for signs of compromise on every node: F6 names a
nodeup '[email protected]'entry in the Erlang system log (erlang.log) as a key indicator; it also lists two IP addresses and a staging path. Look back at least to 21 October, when Cisco published the flaw. - If you find the entry, review the other logs on the device and the systems behind it, and change credentials the attackers could have reached. In the F6 case they went from two internet-facing devices to two cluster nodes on the internal network.
- Don't: treat a clean edge device as proof of a clean network behind it.
What we know – and what we don't
- Cisco rates the flaw 9.8. It comes from persistent cookies and from client certificates not being validated when TLS Verify Mode for clustering is enabled; with the cookies, an attacker can send commands to the database service and run them as root. The CVE record classifies it as hard-coded credentials (CWE-798).
- F6: after gaining root, the attackers ran Python scripts that scanned networks, looked for SMB shares, connected to SQL Server and WinRM and searched GitLab repositories; the goal was credentials and other sensitive data. F6 thinks AI tools helped write them, judging by their comments.
- The attack has not been linked to a known group.
- Conflict: Cisco's advisory, still at version 1.0 on 21 November, says Cisco is not aware of malicious use; F6 reports exploitation and CISA lists the flaw as exploited, with a 23 November deadline for US federal agencies.
- Not known: how many organisations have been hit beyond the one F6 describes.
Why it matters
Video gateways at the network edge are, in our view, easy to leave out of the monthly patch routine. Here a month passed between the fix and the first reported use, and from the edge devices the attackers reached cluster nodes on the internal network.