Does this concern you?
- Affected: anyone whose VPN or remote-access gateway is Ivanti Connect Secure.
- Skip it if: your VPN is not Ivanti Connect Secure.
What to do
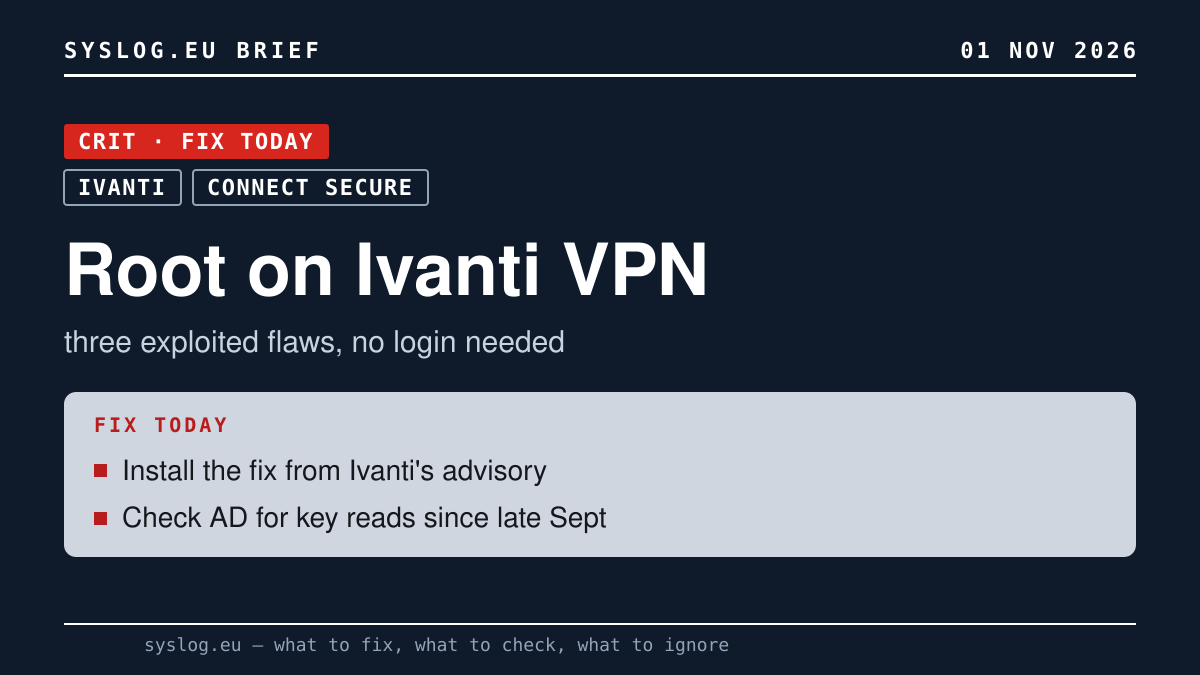
- Install the fixed release for your branch from Ivanti's advisory today. 22.8R2.5 closed only the authentication bypass, per the CVE record; LavX says 22.8R2.6 fixes the other two. On the newer branch the numbers conflict: LavX names 25.1.1.3, the CVE record lists the higher 25.1.3.0 and 25.1.3.1 as not affected by the bypass. Ivanti patched the privilege escalation on October 29.
- No fix for your version yet? CISA's instruction is to stop using the product until there is one.
- Don't rely on the appliance's logs: Volexity says the attackers deleted evidence from Ivanti debug logs and Linux audit logs. Watch for large numbers of requests to /dana-na/auth/url_default/welcome.cgi and search Active Directory from late September for any service account reading LAPS passwords or BitLocker recovery keys, and for Kerberoasting. In our view, start with the account the VPN uses.
- Found signs, or connections from the VPN to other machines? Volexity advises a forensic investigation; CISA requires forensic triage from US agencies. In our view, also change the passwords of the VPN's AD account and of any account seen reading those secrets, and rotate the LAPS passwords and BitLocker recovery keys.
- Don't: read the US deadlines, Nov 2 and Nov 13, as a grace period; Volexity found the attacks in early October.
What we know – and what we don't
- The chain, per CISA and the CVE records: CVE-2026-104935, an authentication bypass rated 8.6 that lets a remote attacker run commands without logging in; CVE-2026-118527, which lets an authenticated user upload files to a known location; and CVE-2026-111357, which lets a local user escalate to root.
- CVE-2026-111357 is rated 8.8 by The Hacker News (repeated by LavX) and 7.0 in Ivanti's CVE record. CVE-2026-118527 had no published CVE record on October 31; its details come from CISA's catalog.
- Volexity found the group, UTA0576, on an appliance fully patched at the time (22.8R2.4).
- Motive: Volexity leans, with low confidence, to criminal; LavX says espionage.
Why it matters
A VPN gateway is trusted by everything behind it. A patch closes the hole; it does not show whether someone already used it, or change a stolen password. Patch today, then look where these attackers went: the directory.